Field Notes

Two cyan approval seals hover above a transaction slab whose internal amber route has changed.

The Payment You Approved Can Change: How Stale Approvals Break Dual Control

An approval attached to an editable request can authorize a different payment, refund, or infrastructure change. Learn how stale approvals work and how immutable instructions, independent review, and transactional release protect your business.
An API hub pours amber usage tokens through an open valve into a growing pile.

Unrestricted API Spending: When Your Website Becomes a Blank Check

A public feature can trigger paid API work without exposing a key. Learn how atomic budgets, bounded jobs, and rate limits contain the cost.

One identity controls two account cards that feed separate approval gates.

Approval Bypass: When Two Accounts Are Still One Person

A workflow can log two usernames and still let one person authorize a risky change. Learn how to detect self-approval and build enforceable, auditable two-person controls.

An amber payment instruction enters a timeline after a cyan instruction has passed approval.

The Payment You Approved Can Change Before It Runs: How Stale Approvals Bypass Business Controls

An approved payment can change before release. Learn how stale approvals undermine business controls and how version-bound review prevents unapproved changes.

Amber records remain visible inside a cyan database behind cleared outer tiles.

Deleted Does Not Mean Gone: The Customer Data Still Hiding in Your Database

Deleted records can leave readable data in database files, transaction logs, and backups. Learn how to test the gap and build a verified deletion workflow.

A cyan production database is mirrored into a smaller amber-edged testing chamber across a glass divide.

Production-data clones expose staging environments

Copying a production database into staging can quietly duplicate customer, employee, and transaction data into a weaker environment. Learn how the exposure happens, how to audit it safely, and how synthetic data, minimization, isolation, and verified cleanup reduce the risk.

An amber stream concealed in a frosted document diverts a cyan automated workflow.

Indirect prompt injection in AI automation

An AI assistant that reads emails, tickets, documents, webpages, or CRM records can mistake attacker-controlled text for instructions. Learn how indirect prompt injection crosses trust boundaries—and how deterministic policy, least privilege, exact approval, provenance, and monitoring keep model output from becoming unauthorized business authority.

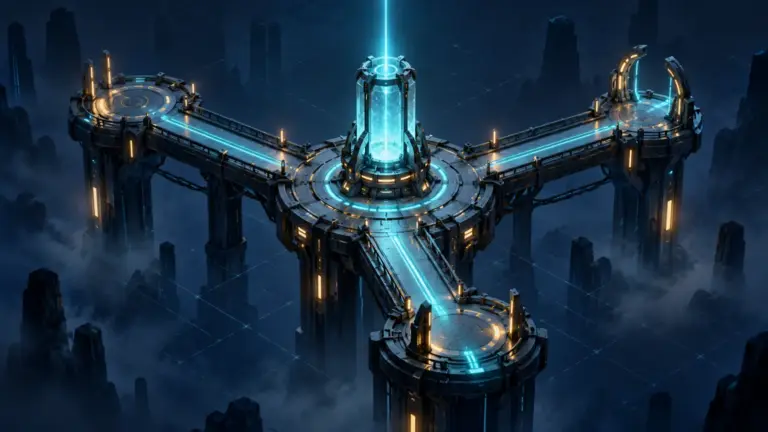
A cyan transmission beacon rises above an isometric relay station with branching illuminated routes.

0FZ: every route through NARROW-17

A complete, spoiler-marked walkthrough of 0FZ Transmission One, including every puzzle solution, optional record, casualty path, J-0 route, final choice, accessibility mode, and lesson hidden inside NARROW/17.

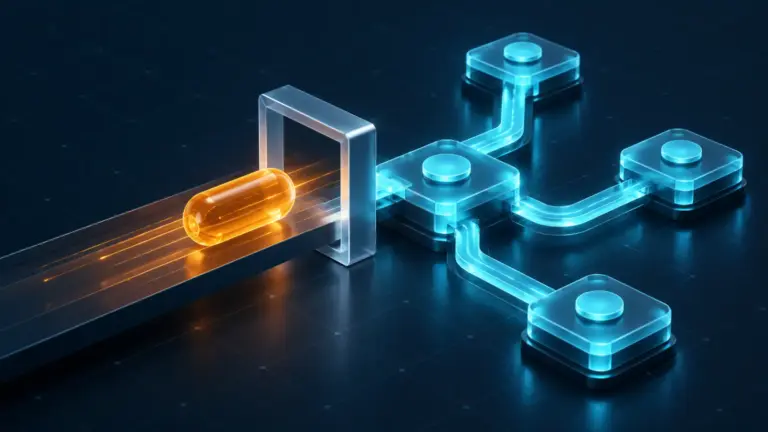
An amber event capsule passes through an open gateway into a cyan automation junction.

Forged webhooks and unsigned events

An endpoint that trusts incoming JSON can be tricked into marking orders paid, granting access, or launching automations. Learn how forged webhooks work and how signatures, replay controls, idempotency, account binding, and state validation protect the business.

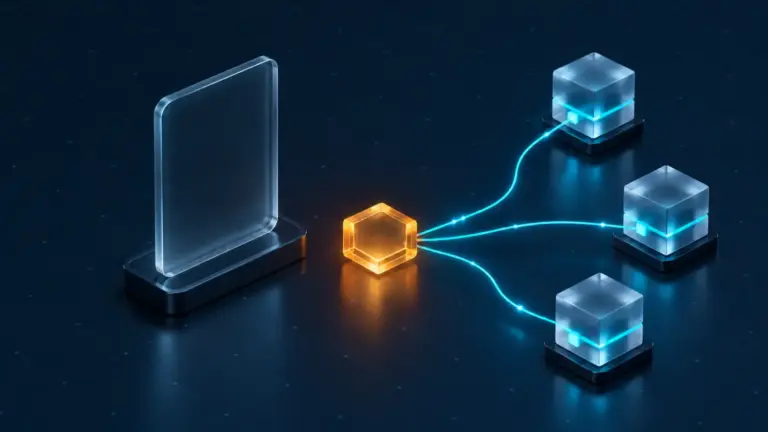
An access token remains connected to three network nodes beside an empty identity frame.

Orphaned OAuth tokens after employee offboarding

Disabling a former worker’s main login may not revoke every session, OAuth grant, personal token, shared credential, or standalone account. Learn how lingering access works, how to audit it safely, and how to build offboarding that produces verifiable evidence.